First Pass

11 stories from 10 sources

France raises stakes after Iran-linked civilian cyberattacks

Day’s Recap

Supporting Articles

French intelligence identifies Shahid Kaveh as an Iran-linked cyber unit operating through front groups that present themselves as vigilante hackers. The groups allegedly target Iran’s adversaries while obscuring the role of the Islamic Revolutionary Guard Corps.

9:27 AMAl Jazeera
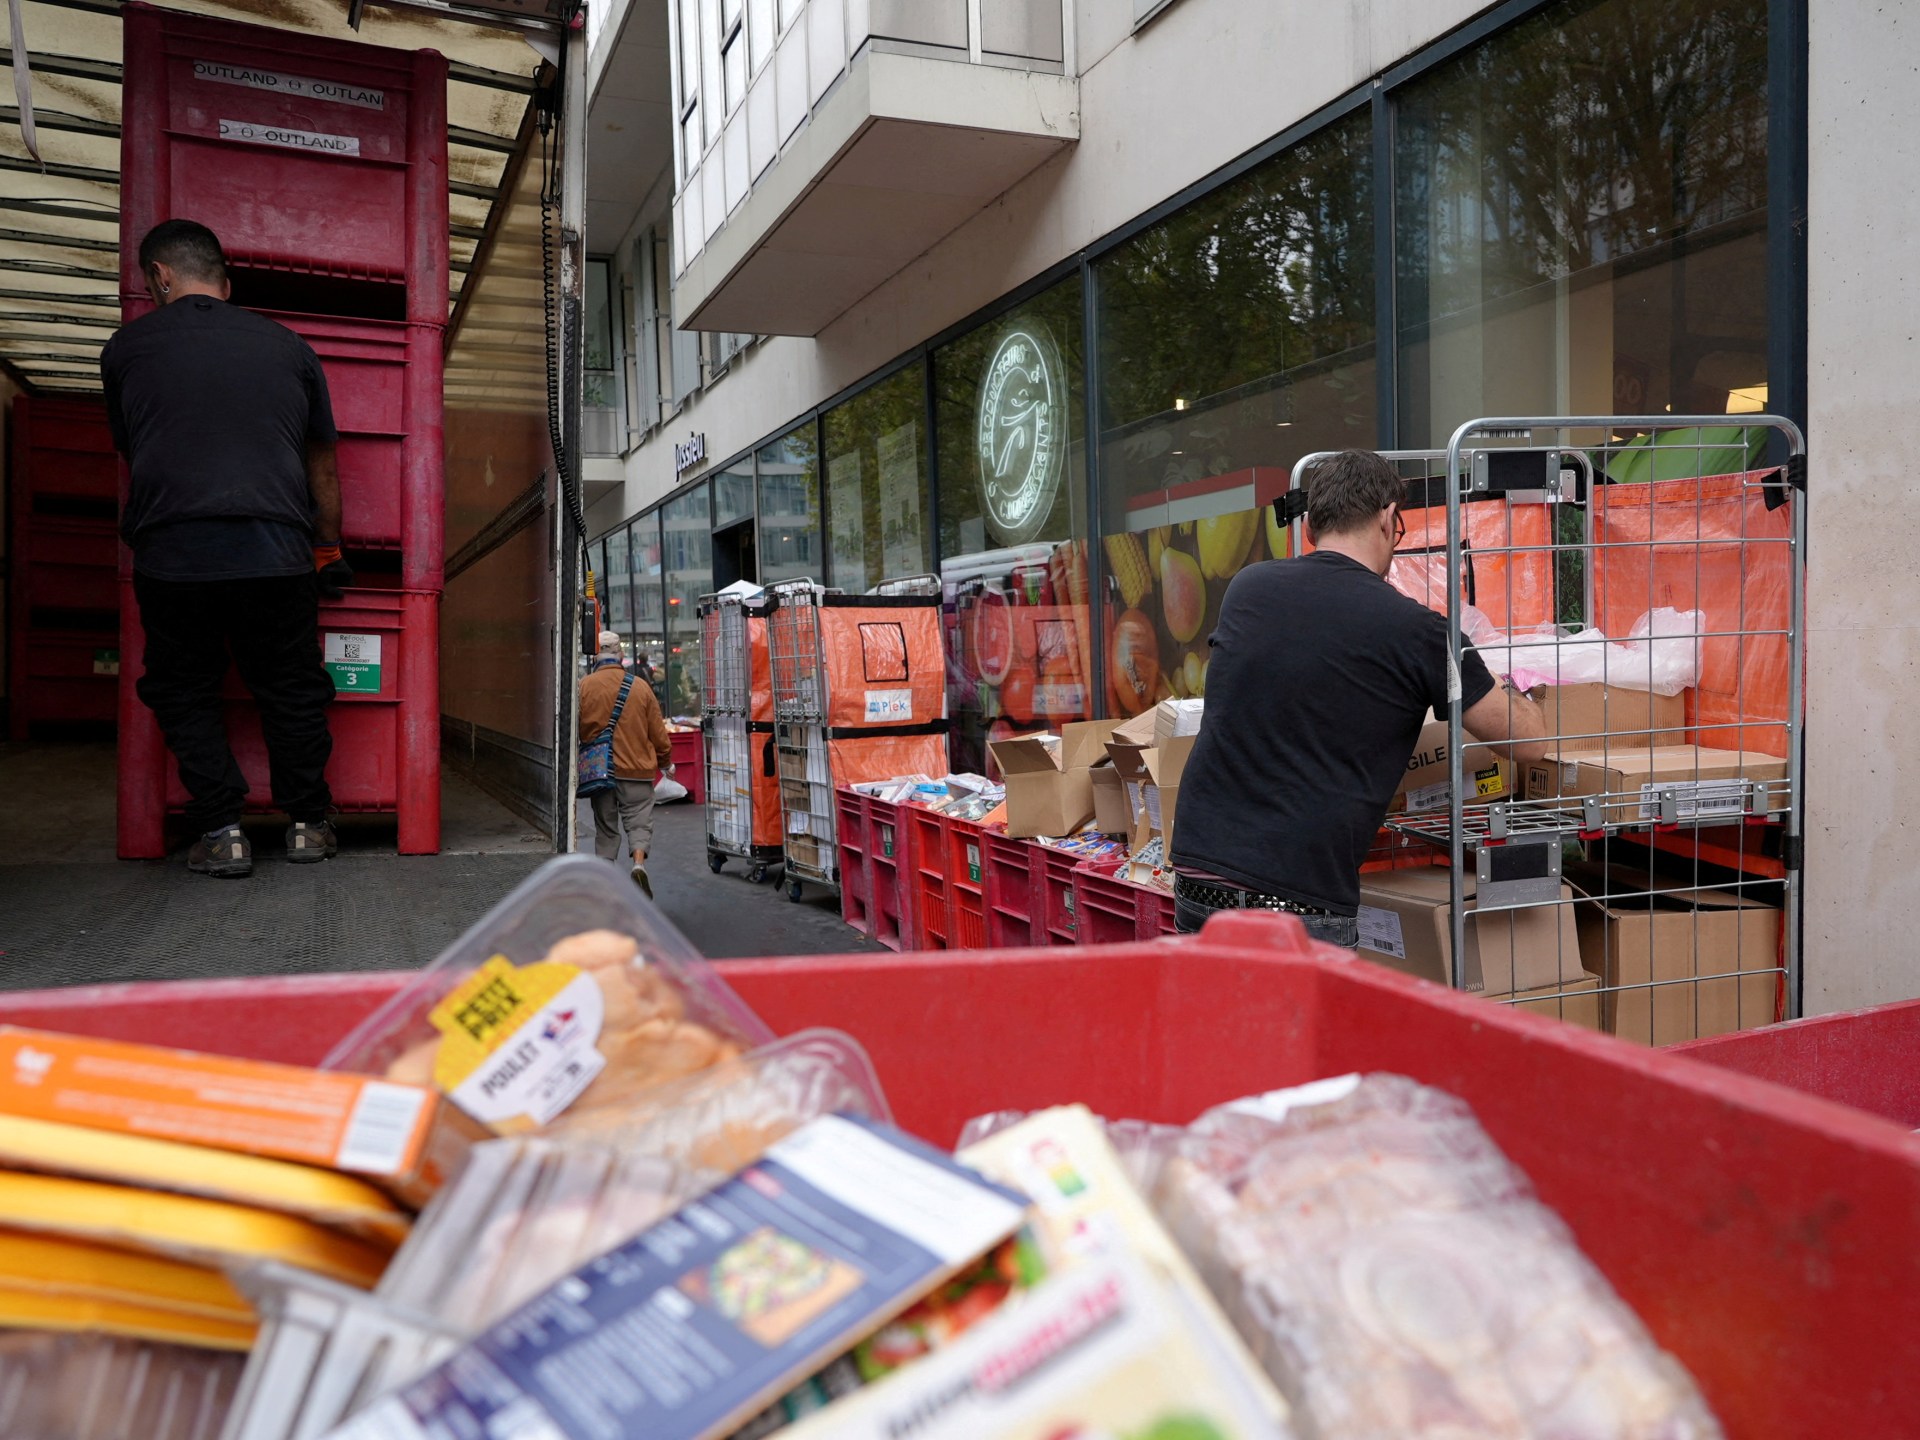
France says the cyber unit of Iran's Islamic Revolutionary Guard Corps carried out an unprecedented campaign against supermarket refrigerators, causing millions of euros in damage. Paris is considering sanctions in response.

8:43 AMCNBC

Microsoft released fixes for nearly 1,100 vulnerabilities across Windows and supported software, including 63 critical flaws and a zero-day affecting Outlook. Adobe, Apple, Google, and Mozilla also issued security updates.

4:55 PMKrebs on Security

Australia has unveiled a new artificial intelligence regulator following a breach involving OpenAI. The government is also considering criminal penalties for companies whose models engage in harmful conduct.

6:01 AMThe New York Times

Other Developments

A curated list of other prominent stories from this day.

A researcher found roughly 35,000 applications created with Grok Build that were publicly accessible to anyone who searched for them. The exposed apps contained confidential information, including data linked to SpaceX.

4:12 PMArs Technica

Congress returns with expiring cybersecurity authorities and unfinished AI safety legislation competing for limited floor time. Republicans have only a few weeks to act before Democrats take control of both chambers in January.

1:46 PMPYMNTS

Nintendo’s latest Switch 2 firmware update blocks a jailbreak that gave hackers access to system files and game ROMs. The company is moving quickly to close the exploit and protect its platform.

12:51 PMPolygon

Hugging Face executive Irene Solaiman warns that rising cyberattacks against open AI platforms could lead operators to impose tighter security controls and restrict access to models and tools.

8:00 AMTechCrunch

A decade-old flaw involving OpenSSH and musl allows attackers to bypass disabled password authentication on certain Alpine Linux and other musl-based accounts by submitting a password longer than 256 bytes.

7:02 AMSchneier on Security

Make it yours

Build Your First Pass.

Pick your topics, set your cadence, and receive your personalized First Pass in your inbox. It’s that simple!